
Pale Moon (32bit)25.8.0
 免费下载
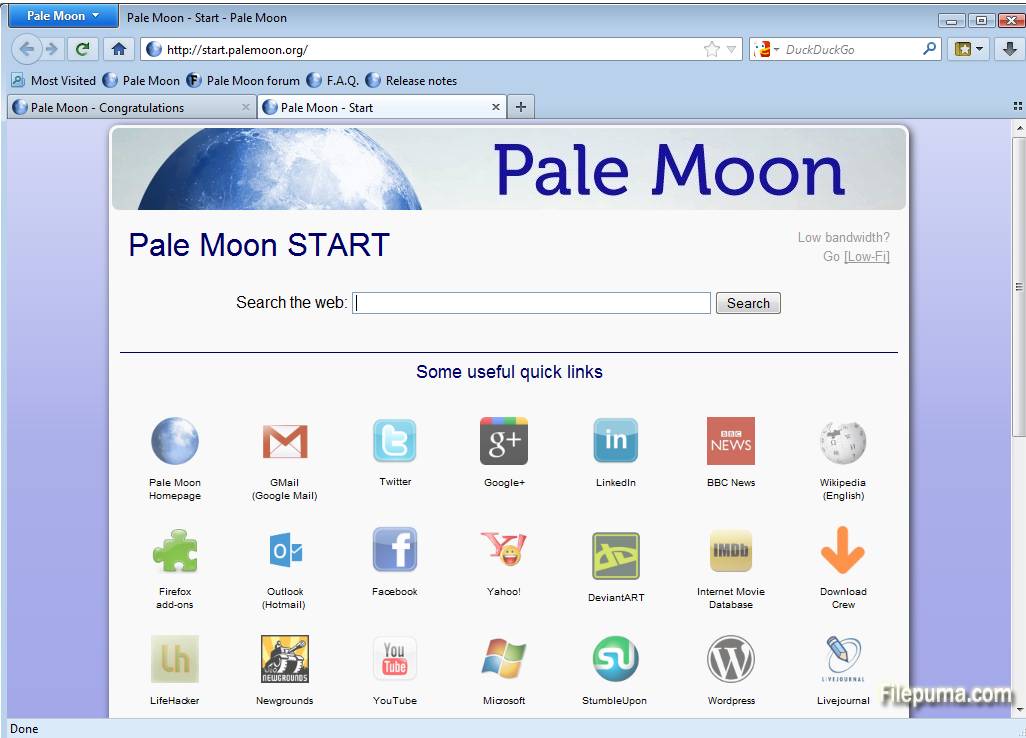
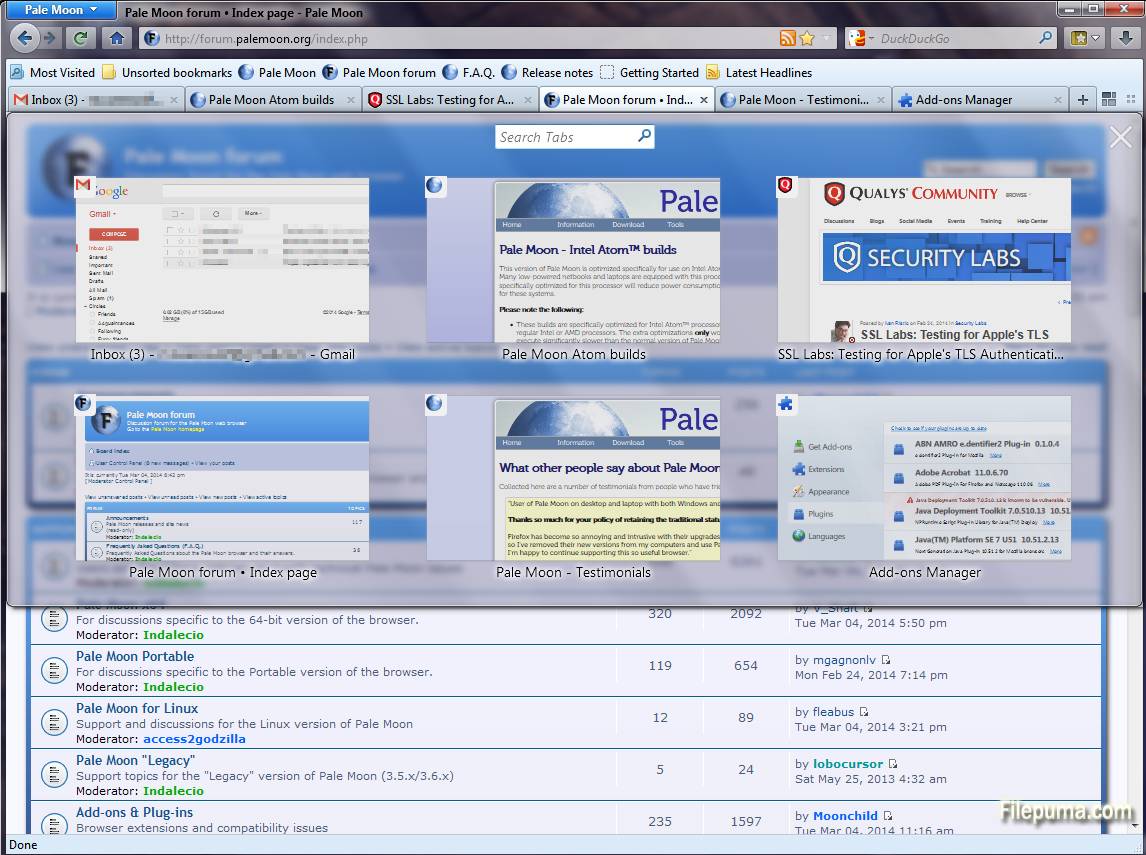
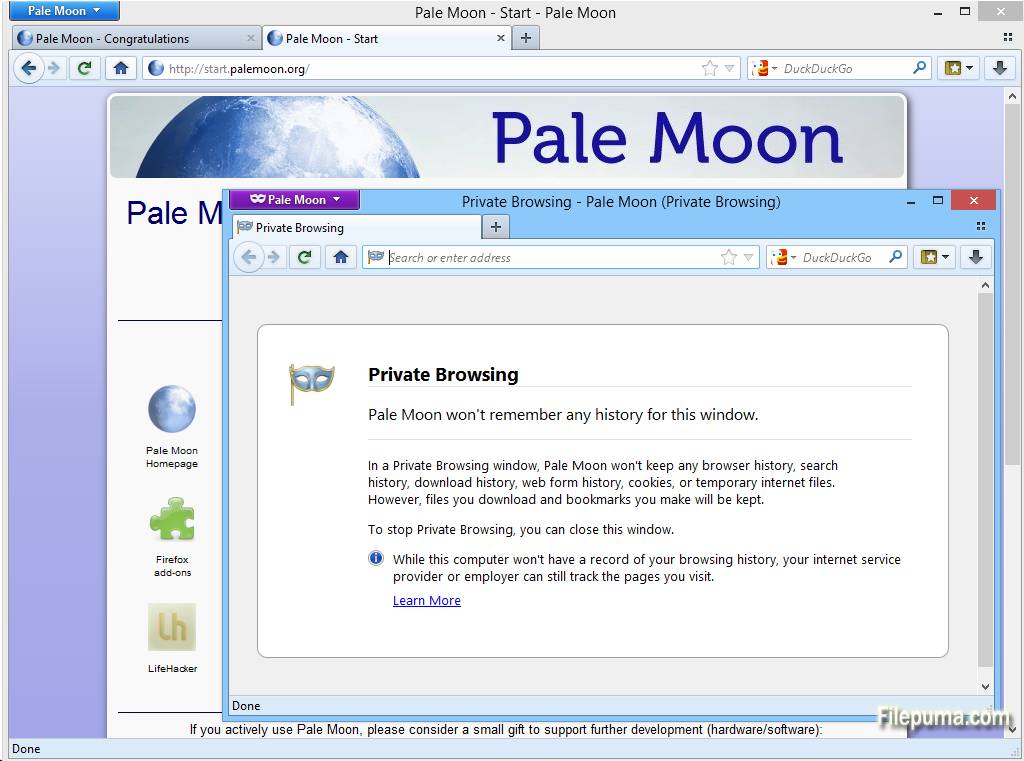
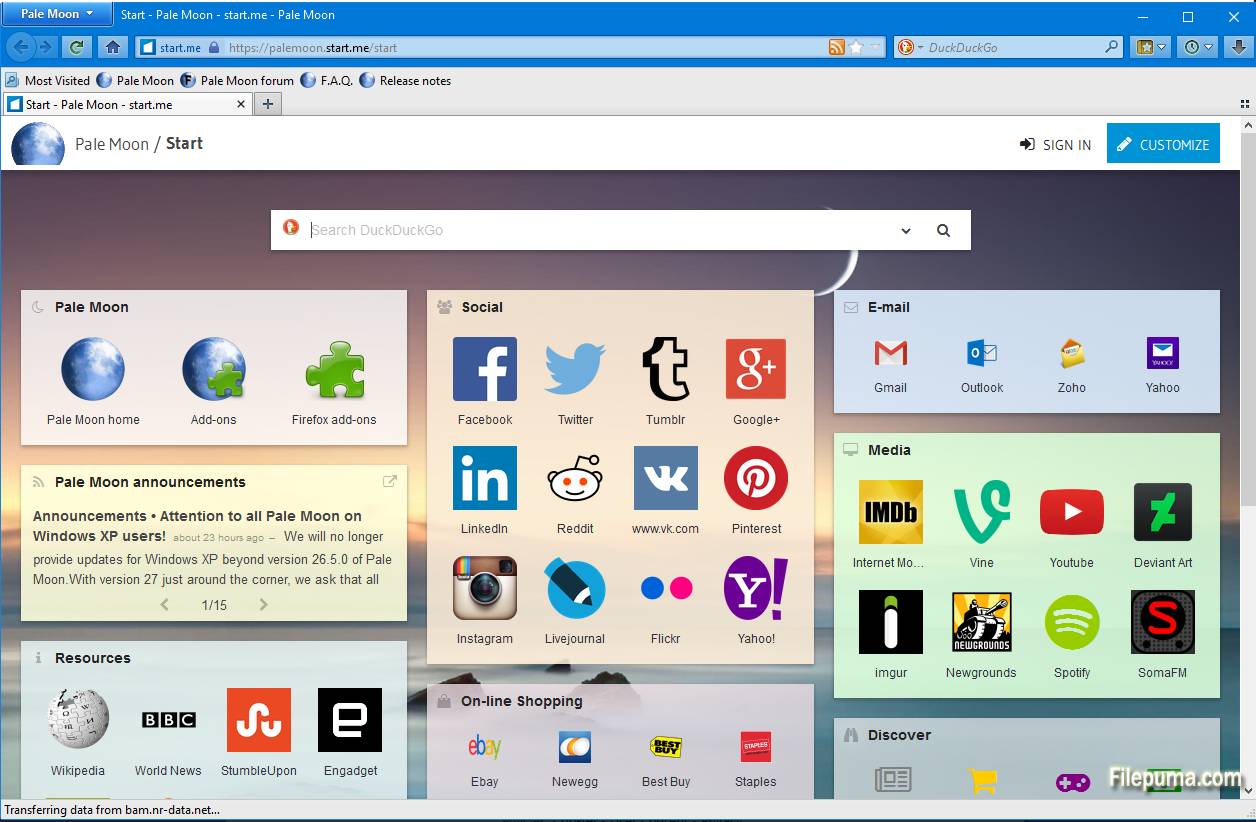


苍月浏览器是一个开源的、基于Firefox的适用于Microsoft Windows的网页浏览器,专注于效率和易用性。确保充分利用你的浏览器!
Pale Moon为您提供一种浏览体验,该浏览器完全从源代码构建,精心挑选了功能和优化,以最大化浏览器的速度、稳定性和用户体验,同时保持与您钟爱和依赖的数千个Firefox扩展的兼容性。
这个浏览器虽然在工作方式上与Firefox接近,但它提供了一套不同的功能。某些精心挑选的、不太受欢迎且不影响网页显示或功能的功能被禁用;所有这些都是为了最大限度地提高浏览器的效率。请参阅技术细节页面,以了解浏览器具体支持和不支持的功能。例如,如果您需要辅助功能或家长控制,请访问Firefox主页并获取官方的、未优化版本的浏览器。
主要特点:
Pale Moon为您提供一种浏览体验,该浏览器完全从源代码构建,精心挑选了功能和优化,以最大化浏览器的速度、稳定性和用户体验,同时保持与您钟爱和依赖的数千个Firefox扩展的兼容性。
这个浏览器虽然在工作方式上与Firefox接近,但它提供了一套不同的功能。某些精心挑选的、不太受欢迎且不影响网页显示或功能的功能被禁用;所有这些都是为了最大限度地提高浏览器的效率。请参阅技术细节页面,以了解浏览器具体支持和不支持的功能。例如,如果您需要辅助功能或家长控制,请访问Firefox主页并获取官方的、未优化版本的浏览器。
Pale Moon将继续提供适当大小的分组导航按钮、默认启用的书签工具栏、与默认页面内容相邻的选项卡(易于切换),至少没有功能状态栏和更多的自定义自由,仅举几例。
Pale Moon 是并将永远是开源的,可以完全免费下载和使用!
主要特点:
- 为现代处理器优化
- 基于包含我们自己优化的布局和渲染引擎(Goanna)的Unified XUL Platform(UXP)
- 安全:从成熟的Mozilla代码派生,并定期更新最新的安全补丁
- 安全:附加的安全功能和安全意识开发
- 由我们的用户社区支持,完全非营利
- 注重隐私:无广告;无遥测、间谍软件或数据收集
- 熟悉、高效、完全可定制的界面
- 支持完整主题:任意元素设计的完全自由
- 支持轻松创建的轻量级主题(皮肤)
- 流畅和快速的页面绘制与脚本处理
- 优质的渐变和字体
- 将继续支持NPAPI插件如Silverlight、Flash和Java
- 支持越来越多的Pale Moon独占扩展
- 广泛且日益增长的对现有网络标准的支持
有什么新鲜事
Version 25.8.0
Fixes/changes:
Security fixes:
Fixes/changes:
- Updated LibVPX to 1.4.x to be able to play more kinds of VP9-encoded videos.
- Updated the JPEG decoder library to 1.4.0.
- Fixed and cleaned up XPCOM timer thread code to avoid intermittent issues with events not firing (especially after stand-by).
- Updated overrides to work around issues with Facebook and Netflix.
- Fixed an issue where too-old system-supplied NSPR and/or NSS libraries would be accepted for use.
Security fixes:
- Updated the libpng library to 1.5.24 to address critical security issues CVE-2015-7981 and CVE-2015-8126
- Updated the NSPR library to 4.10.10 to address several security issues.
- Updated the NSS library to 3.19.4 to address several security issues.
- Fixed a memory safety hazard in SVG path code (CVE-2015-7199).
- Fixed an issue with IP address parsing potentially allowing an attacker to bypass the Same Origin Policy (CVE-2015-7188).
- Fixed an Add-on SDK (Jetpack) issue that would allow scripts to be executed despite being forbidden (CVE-2015-7187).
- Fixed a crash due to a buffer underflow in libjar (CVE-2015-7194).
- Fixed an issue for Android full screen that would potentially allow address spoofing (CVE-2015-7185).
- Added size checks in canvas manipulations to avoid potential image encoding vulnerabilities like CVE-2015-7189. DiD
- Fixed potential information disclosure vulnerabilities through the NTLM authentication mechanism. Insecure NTLM v1 is now disabled by default, and the workstation name is set to WORKSTATION by default (configurable with a preference for environments where identification of workstations is done by actual reported machine name). This avoids issues like CVE-2015-4515.
- Fixed a potentially vulnerable crash from a spinning event loop during resize painting. DiD
- Fixed several Javascript-based memory safety hazards. DiD
该程序可提供其他语言版本。
- Download Pale Moon (32bit)
- Télécharger Pale Moon (32bit)
- Herunterladen Pale Moon (32bit)
- Scaricare Pale Moon (32bit)
- ダウンロード Pale Moon (32bit)
- Descargar Pale Moon (32bit)
- Baixar Pale Moon (32bit)
用户评论
用户评分
4/5
 46
许可证:
免费
要求:
Windows Vista/ Windows 7/ Windows 8/ Windows 10/ Server 2008
语言:
English
尺寸:
20.4MB
出版商:
已更新:
Nov 17, 2015
清洁
报告软件
最新版本
旧版本
 Pale Moon (32bit) 34.3.2
 Pale Moon (64bit) 34.3.2
 FossaMail (32bit) 38.2.0
 FossaMail (64bit) 38.2.0
 Pale Moon Portable (32bit) 34.3.2
 Pale Moon Portable (64bit) 34.3.2
 Google Chrome (64bit) 153.0.8010.48
 Google Chrome (32bit) 153.0.8010.48
 Mozilla Firefox (32bit) 156.0
 Mozilla Firefox (64bit) 156.0
 Maxthon (64bit) 7.5.3.2200
安全级别
为了避免对您的设备造成潜在危害,并确保您的数据和隐私的安全,我们团队在每次新的安装文件上传到我们的服务器或链接到远程服务器时都会进行检查,并定期审查该文件以确认或更新其状态。基于这些检查,我们为所有可下载文件设置了以下安全级别。
 清洁
这个软件程序很可能是干净的。
我们在全球60多款领先的 antivirus 服务中扫描了与该软件程序相关的文件和 URL;没有发现任何潜在威胁。同时也没有捆绑任何第三方软件。
 警告
该程序是由广告支持的,可能会提供安装不必要的第三方程序。这些程序可能包括工具栏、更改主页、默认搜索引擎或安装其他第三方程序。这些可能是误报,我们建议用户在安装和使用该软件时要小心。
 残疾人
该软件不再提供下载。该软件程序很可能是恶意的,或者存在安全问题或其他原因。
提交报告
谢谢!
您的报告已发送。
我们将审核您的请求并采取适当的措施。
请注意,您将不会收到有关此报告所采取任何行动的通知。对于可能造成的任何不便,我们深表歉意。
我们感谢您帮助保持我们网站的整洁和安全。