Looking for a free Mac cleaner? Try diCleaner

Pidgin2.10.10
 免费下载
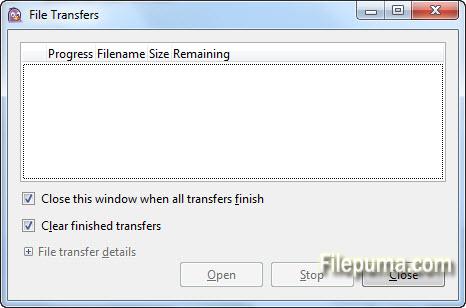
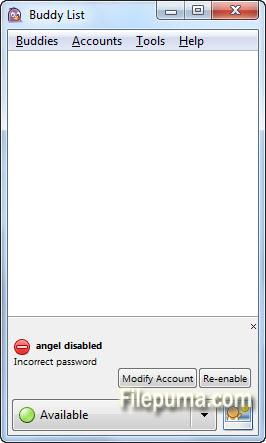
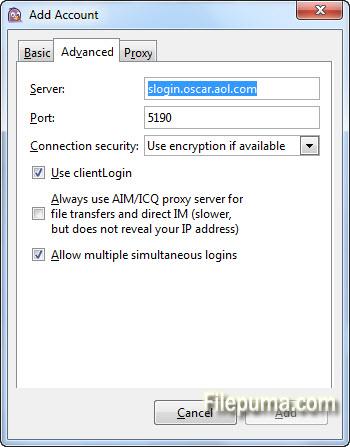
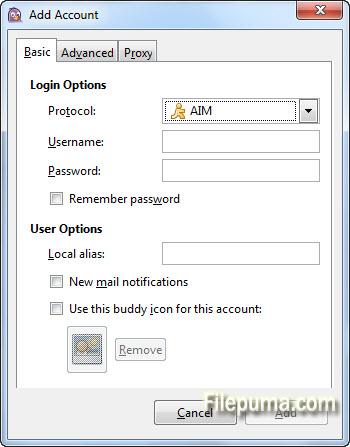


皮钦是一款广泛使用的即时通讯应用程序,促进来自不同语言背景的用户之间的交流。Pidgin以简单和易用性为设计理念,支持多种聊天协议,包括AIM、ICQ、Google Talk、XMPP等,允许用户将多个账户整合到一个界面中。
Pidgin 的其中一个关键特性是其自定义选项。用户可以通过选择各种主题和插件来个性化他们的体验,以增强功能。无论是添加表情符号、整合加密以确保会话安全,还是扩展对其他聊天协议的支持,Pidgin 提供了满足个人偏好的灵活性。
Pidgin的另一个显著特点是其开源性质,这促进了社区内的协作和创新。全球的开发者为其改进做出贡献,确保定期更新和修复漏洞,以保持其可靠性和性能。
Pidgin 的用户友好界面使其适合于休闲和专业使用。对于那些寻求超越语言障碍的流线型沟通平台的个人、企业和组织来说,它深受青睐。
总之,Pidgin作为一种多功能且易于访问的即时通讯解决方案,使用户能够在不同的平台和协议上无缝连接和沟通。
主要功能:
- 支持多种协议:可同时连接到多个聊天网络。
- 可自定义界面:用户可以个性化主题、字体和布局。
- 插件系统:通过可下载的插件扩展功能。
- 文件传输:在用户之间安全发送文件。
- 表情符号和笑脸:聊天时可用的丰富表情符号。
- 聊天记录:记录并保存聊天对话。
- 加密和安全:支持私人对话的加密。
- 状态信息:显示在线、离开、忙碌或离线状态。
有什么新鲜事
- Check the basic constraints extension when validating SSL/TLS certificates. This fixes a security hole that allowed a malicious man-in-the-middle to impersonate an IM server or any other https endpoint. This affected both the NSS and GnuTLS plugins. (Discovered by an anonymous person and Jacob Appelbaum of the Tor Project, with thanks to Moxie Marlinspike for first publishing about this type of vulnerability. Thanks to Kai Engert for guidance and for some of the NSS changes) (CVE-2014-3694)
- Allow and prefer TLS 1.2 and 1.1 when using the NSS plugin for SSL. (Elrond and Ashish Gupta)
libpurple3 compatibility
- Encrypted account passwords are preserved until the new one is set.
- Fix loading Google Talk and Facebook XMPP accounts.
Windows-Specific Changes
- Don't allow overwriting arbitrary files on the file system when the user installs a smiley theme via drag-and-drop. (Discovered by Yves Younan of Cisco Talos) (CVE-2014-3697)
- Updates to dependencies
- NSS 3.17.1 and NSPR 4.10.7
Finch
- Fix build against Python 3. (Ed Catmur)
Gadu-Gadu
- Updated internal libgadu to version 1.12.0.
Groupwise
- Fix potential remote crash parsing server message that indicates that a large amount of memory should be allocated. (Discovered by Yves Younan and Richard Johnson of Cisco Talos) (CVE-2014-3696)
IRC
- Fix a possible leak of unencrypted data when using /me command with OTR. (Thijs Alkemade)
MXit
- Fix potential remote crash parsing a malformed emoticon response. (Discovered by Yves Younan and Richard Johnson of Cisco Talos) (CVE-2014-3695)
XMPP
- Fix potential information leak where a malicious XMPP server and possibly even a malicious remote user could create a carefully crafted XMPP message that causes libpurple to send an XMPP message containing arbitrary memory. (Discovered and fixed by Thijs Alkemade and Paul Aurich) (CVE-2014-3698)
- Fix Facebook XMPP roster quirks.
Yahoo
- Fix login when using the GnuTLS library for TLS connections.
该程序可提供其他语言版本。
- Download Pidgin
- Télécharger Pidgin
- Herunterladen Pidgin
- Scaricare Pidgin
- ダウンロード Pidgin
- Descargar Pidgin
- Baixar Pidgin
用户评论
用户评分
 4
许可证:
免费
要求:
Windows All
语言:
Multi-languages
尺寸:
9.2MB
出版商:
已更新:
Oct 22, 2014
清洁
报告软件
最新版本
旧版本
开发者软件
 Pidgin 2.14.14
 TeamSpeak Client (64bit) 3.6.2
 Telegram Desktop 7.2.8
 TeamSpeak Client (32bit) 3.6.2
 Signal 8.26.0
 Mumble 1.5.915
安全级别
为了避免对您的设备造成潜在危害,并确保您的数据和隐私的安全,我们团队在每次新的安装文件上传到我们的服务器或链接到远程服务器时都会进行检查,并定期审查该文件以确认或更新其状态。基于这些检查,我们为所有可下载文件设置了以下安全级别。
 清洁
这个软件程序很可能是干净的。
我们在全球60多款领先的 antivirus 服务中扫描了与该软件程序相关的文件和 URL;没有发现任何潜在威胁。同时也没有捆绑任何第三方软件。
 警告
该程序是由广告支持的,可能会提供安装不必要的第三方程序。这些程序可能包括工具栏、更改主页、默认搜索引擎或安装其他第三方程序。这些可能是误报,我们建议用户在安装和使用该软件时要小心。
 残疾人
该软件不再提供下载。该软件程序很可能是恶意的,或者存在安全问题或其他原因。
提交报告
谢谢!
您的报告已发送。
我们将审核您的请求并采取适当的措施。
请注意,您将不会收到有关此报告所采取任何行动的通知。对于可能造成的任何不便,我们深表歉意。
我们感谢您帮助保持我们网站的整洁和安全。