Looking for a free Mac cleaner? Try diCleaner

Nmap6.45
 निःशुल्क डाउनलोड
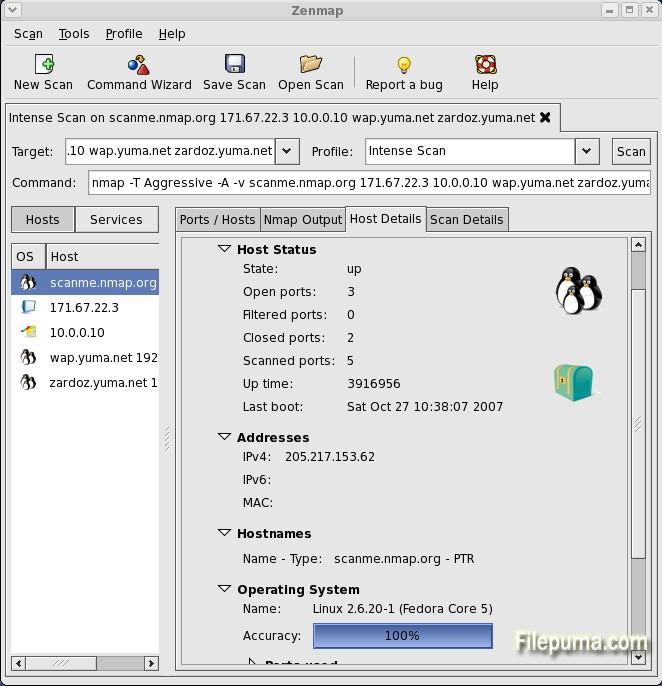
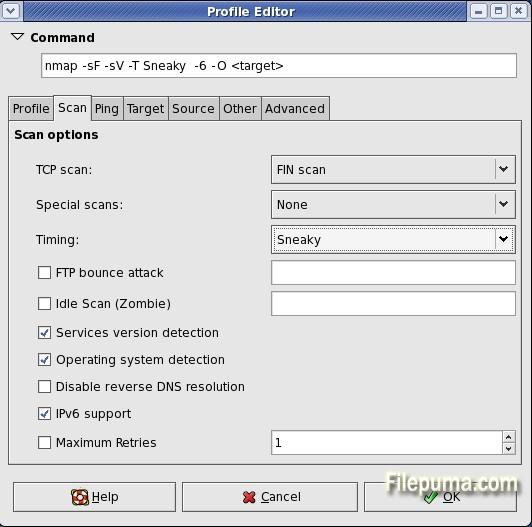


Nmapनेटवर्क मैपर के लिए संक्षिप्त, नेटवर्क खोज और सुरक्षा ऑडिटिंग के लिए डिजाइन किया गया एक व्यापक रूप से उपयोग किया जाने वाला ओपन-सोर्स टूल है। Gordon Lyon द्वारा विकसित, Nmap का उपयोग नेटवर्क प्रशासकों, सुरक्षा पेशेवरों, और हैकर्स द्वारा नेटवर्क स्कैन करने और होस्ट और सेवाओं की पहचान करने के लिए किया जाता है। यह नेटवर्क इन्वेंट्री, सेवा उन्नयन शेड्यूल प्रबंधित करने, और होस्ट या सेवा अपटाइम की निगरानी के लिए अत्यधिक प्रभावी है।
Nmap लक्षित होस्टों को विशेष रूप से निर्मित पैकेट भेजकर और उनके प्रतिक्रियाओं का विश्लेषण करके कार्य करता है। यह प्रक्रिया इसे नेटवर्क पर विभिन्न उपकरणों की स्थिति का निर्धारण करने की अनुमति देती है, जिसमें कौन से पोर्ट खुले हैं, कौन सी सेवाएँ चल रही हैं, और कौन से ऑपरेटिंग सिस्टम उपयोग में हैं। Nmap स्कैनिंग तकनीकों की एक विस्तृत श्रृंखला का समर्थन करता है, जिनमें TCP connect, SYN scan, UDP scan, और OS detection शामिल हैं, जिससे नेटवर्क का गहन विश्लेषण संभव हो पाता है।
Nmap की प्रमुख विशेषताओं में से एक इसका स्क्रिप्टिंग इंजन (NSE) है, जो उपयोगकर्ताओं को ऑटोमेटेड टास्क करने में सक्षम बनाता है जैसे कि कमजोरियों का पता लगाना, मैलवेयर की खोज करना और उन्नत नेटवर्क टोही करना। NSE स्क्रिप्ट्स Lua में लिखी जाती हैं, जो एक हल्की प्रोग्रामिंग भाषा है, जिससे उपयोगकर्ता Nmap की कार्यक्षमता का विस्तार कर सकते हैं और अपनी विशिष्ट आवश्यकताओं के अनुसार स्कैन को कस्टमाइज़ कर सकते हैं।
Nmap कई प्लेटफार्मों पर समर्थित है, जिसमें Windows, macOS, और Linux शामिल हैं, जिससे यह विभिन्न ऑपरेटिंग सिस्टम के उपयोगकर्ताओं के लिए सुलभ होता है। इसकी मजबूत विशेषताएँ और उपयोग में आसानी Nmap को नेटवर्क सुरक्षा आकलनों के लिए एक महत्वपूर्ण उपकरण और कई साइबर सुरक्षा टूलकिट का मूलभूत घटक बनाती हैं।
मुख्य विशेषताएं:
- होस्ट डिस्कवरी: नेटवर्क पर लाइव होस्ट्स का पता लगाता है।
- पोर्ट स्कैनिंग: खुली पोर्ट्स को स्कैन करता है यह देखने के लिए कि कौन-कौन सी सेवाएँ चल रही हैं।
- सेवा संस्करण पहचान: खुले पोर्ट्स पर सॉफ़्टवेयर संस्करणों की पहचान करता है।
- ओएस डिटेक्शन: एक होस्ट की ऑपरेटिंग सिस्टम और डिवाइस प्रकार का पता लगाता है।
- Nmap Scripting Engine (NSE): ऐसे कार्यों के लिए स्क्रिप्ट का उपयोग करता है जैसे कि भेद्यता का पता लगाना और स्वचालन।
- फ़ायरवॉल इवेज़न: स्कैन के दौरान फ़ायरवॉल और सुरक्षा प्रणालियों को बाईपास करता है।
- लचीला आउटपुट: परिणामों के लिए कई प्रारूपों का समर्थन करता है, जैसे कि पाठ, XML, और HTML।
- स्टेल्थ स्कैनिंग: सुरक्षा प्रणालियों द्वारा पहचान से बचने के लिए शांति से स्कैन करता है।
- IPv6 समर्थन: दोनों IPv4 और IPv6 नेटवर्क के साथ काम करता है।
- GUI (Zenmap): आसान उपयोग के लिए एक ग्राफिकल इंटरफ़ेस प्रदान करता है।
क्या नया है?
- [NSE] Add ssl-heartbleed script to detect the Heartbleed bug in OpenSSL
- [NSE] Fixed an error-handling bug in socks-open-proxy that caused it to fail when scanning a SOCKS4-only proxy.
- [NSE] Improved ntp-info script to handle underscores in returned data.
- [NSE] Add quake1-info script for retrieving server and player information from Quake 1 game servers. Reports potential DoS amplification factor.
- [NSE] Add unicode library for decoding and encoding UTF-8, UTF-16, CP437 and other character sets to Unicode code points. Scripts that previously just added or skipped nulls in UTF-16 data can use this to support non-ASCII characters.
- When doing a ping scan (-sn), the --open option will prevent down hosts from being shown when -v is specified. This aligns with similar output for other scan types.
- [Ncat] Added support for socks5 and corresponding regression tests.
- [NSE] Add http-ntlm-info script for getting server information from Web servers that require NTLM authentication.
- Added TCP support to dns.lua.
- Added safe fd_set operations. This makes nmap fail gracefully instead of crashing when the number of file descriptors grows over FD_SETSIZE.
- [NSE] Added tls library for functions related to SSLv3 and TLS messages. Existing ssl-enum-ciphers, ssl-date, and tls-nextprotoneg scripts were updated to use this library.
- [NSE] Add sstp-discover script to discover Microsoft's Secure Socket Tunnelling Protocol
- [NSE] Added unittest library and NSE script for adding unit tests to NSE libraries. See unittest.lua for examples, and run `nmap --script=unittest --script-args=unittest.run -d` to run the tests.
- Updated bundled liblua from 5.2.2 to 5.2.3 (bugfix release)
- Added version detection signatures and probes for a bunch of Android remote mouse/keyboard servers, including AndroMouse, AirHID, Wifi-mouse, and RemoteMouse.
- [NSE] Added allseeingeye-info for gathering information from games using this query protocol. A version detection probe was also added.
- [NSE] Add freelancer-info to gather information about the Freelancer game server. Also added a related version detection probe and UDP protocol payload for detecting the service.
- [Ncat] Fixed compilation when --without-liblua is specified in configure (an #include needed an ifdef guard).
- [NSE] Add http-server-header script to grab the Server header as a last-ditch effort to get a software version. This can't be done as a softmatch because of the need to match non-HTTP services that obey some HTTP requests.
- [NSE] Add rfc868-time script to get the date and time from an RFC 868 Time server.
- [NSE] Add weblogic-t3-info script that detects the T3 RMI protocol used by Oracle/BEA Weblogic. Extracts the Weblogic version, as well
- Fixed a bug in libdnet with handling interfaces with AF_LINK addresses on FreeBSD >9 .Likely affected other *BSDs. Handled by skipping these non-network addresses.
- Fixed a bug with UDP checksum calculation. When the UDP checksum is zero (0x0000), it must be transmitted as 1's-complement -0 (0xffff) to avoid ambiguity with +0, which indicates no checksum was calculated. This affected UDP on IPv4 only.
- [NSE] Removed a fixed value (28428) which was being set for the Request ID in the snmpWalk library function; a value based on nmap.clock_ms will now be set instead.
- [NSE] Add http-iis-short-name-brute script that detects Microsoft IIS servers vulnerable to a file/folder name disclosure and a denial of service vulnerability. The script obtains the "shortnames" of the files and folders in the webroot folder.
- Idle scan now supports IPv6. IPv6 packets don't usually come with fragments identifiers like IPv4 packets do, so new techniques had to be developed to make idle scan possible.
- [NSE] Add http-dlink-backdoor script that detects DLink routers with firmware backdoor allowing admin access over HTTP interface.
- The ICMP ID of ICMP probes is now matched against the sent ICMP ID, to reduce the chance of false matches.
- [NSE] Made telnet-brute support multiple parallel guessing threads, reuse connections, and support password-only logins.
- [NSE] Made the table returned by ssh1.fetch_host_key contain a "key" element, like that of ssh2.fetch_host_key. This fixed a crash in the ssh-hostkey script. The "key" element of ssh2.fetch_host_key now is base64-encoded, to match the format used by the known_hosts file.
- [Nsock] Handle timers and timeouts via a priority queue (using a heap) for improved performance. Nsock now only iterates over events which are completed or expired instead of inspecting the entire event set at each iteration.
- [NSE] Update dns-cache-snoop script to use a new list of top 50 domains rather than a 2010 list.
- [NSE] Added the qconn-exec script , which tests the QNX QCONN service for remote command execution.
- [Zenmap] Fixed a crash that would happen when you entered a search term starting with a colon: "AttributeError: 'FilteredNetworkInventory' object has no attribute 'match_'".
- [Ncat] Added NCAT_PROTO, NCAT_REMOTE_ADDR, NCAT_REMOTE_PORT, NCAT_LOCAL_ADDR and NCAT_LOCAL_PORT environment variables being set in all --*-exec child processes.
अन्य भाषाओं में उपलब्ध प्रोग्राम
- Download Nmap
- Télécharger Nmap
- Herunterladen Nmap
- Scaricare Nmap
- ダウンロード Nmap
- Descargar Nmap
- Baixar Nmap
उपयोगकर्ता समीक्षाएं
उपयोगकर्ता रेटिंग
 7
लाइसेंस:
मुक्त
आवश्यकताएँ:
Windows All
भाषाएँ:
English
आकार:
25.6MB
प्रकाशक:
अपडेटेड:
Apr 14, 2014
साफ
रिपोर्ट सॉफ़्टवेयर
नवीनतम संस्करण
पुराने संस्करण
डेवलपर का सॉफ्टवेयर
 Nmap 7.991
 Agnitum Outpost Security Suite 9.1
सुरक्षा स्तर
अपने डिवाइस को किसी संभावित नुकसान से बचाने और आपके डेटा और गोपनीयता की सुरक्षा सुनिश्चित करने के लिए, हमारी टीम हर बार नए इंस्टॉलेशन फ़ाइल को हमारे सर्वरों पर अपलोड करने या किसी दूरस्थ सर्वर से लिंक करने पर जांच करती है और फ़ाइल की स्थिति की पुष्टि या अपडेट करने के लिए समय-समय पर उसकी समीक्षा करती है। इस जांच के आधार पर, हम किसी भी डाउनलोड करने योग्य फ़ाइलों के लिए निम्नलिखित सुरक्षा स्तर निर्धारित करते हैं।
 साफ
यह बहुत अधिक संभावना है कि यह सॉफ़्टवेयर प्रोग्राम स्वच्छ है।
हमने इस सॉफ़्टवेयर प्रोग्राम से संबंधित फ़ाइलों और यूआरएल को दुनिया की 60 से अधिक प्रमुख एंटीवायरस सेवाओं में स्कैन किया; कोई संभावित खतरे नहीं मिले। और कोई तीसरा पक्ष सॉफ़्टवेयर नहीं जोड़ा गया है।
 चेतावनी
यह प्रोग्राम विज्ञापन द्वारा समर्थित है और इसमें तीसरे पक्ष के प्रोग्राम स्थापित करने का प्रस्ताव हो सकता है जो आवश्यक नहीं हैं। इनमें एक टूलबार, आपकी होमपेज को बदलना, डिफ़ॉल्ट खोज इंजन बदलना, या अन्य पार्टी प्रोग्राम स्थापित करना शामिल हो सकते हैं। ये गलत सकारात्मक हो सकते हैं, और हमारे उपयोगकर्ताओं को इस सॉफ़्टवेयर को स्थापित और उपयोग करते समय सावधान रहने की सलाह दी जाती है।
 अक्षम
यह सॉफ्टवेयर अब डाउनलोड के लिए उपलब्ध नहीं है। यह अत्यधिक संभावना है कि इस सॉफ्टवेयर प्रोग्राम में मालिशियस या सुरक्षा समस्याएँ या अन्य कारण हो सकते हैं।
एक रिपोर्ट जमा करें
धन्यवाद!
आपकी रिपोर्ट भेज दी गई है।
हम आपके अनुरोध की समीक्षा करेंगे और उचित कार्रवाई करेंगे।
कृपया ध्यान दें कि आपको इस रिपोर्ट के कारण किए गए किसी भी कार्रवाई के बारे में कोई सूचना नहीं मिलेगी। इसके कारण होने वाले किसी भी असुविधा के लिए हम क्षमा चाहते हैं।
हम आपकी मदद के लिए आभारी हैं जो हमारी वेबसाइट को साफ और सुरक्षित रखने में है।