
Pale Moon (32bit)25.8.0
 免費下載
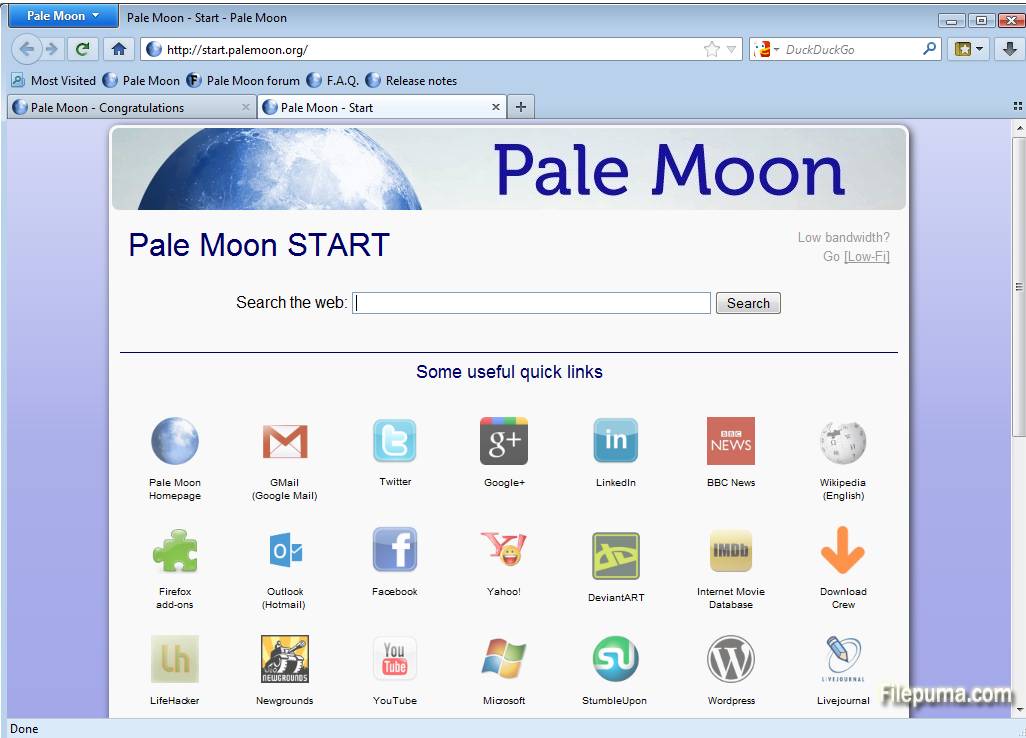
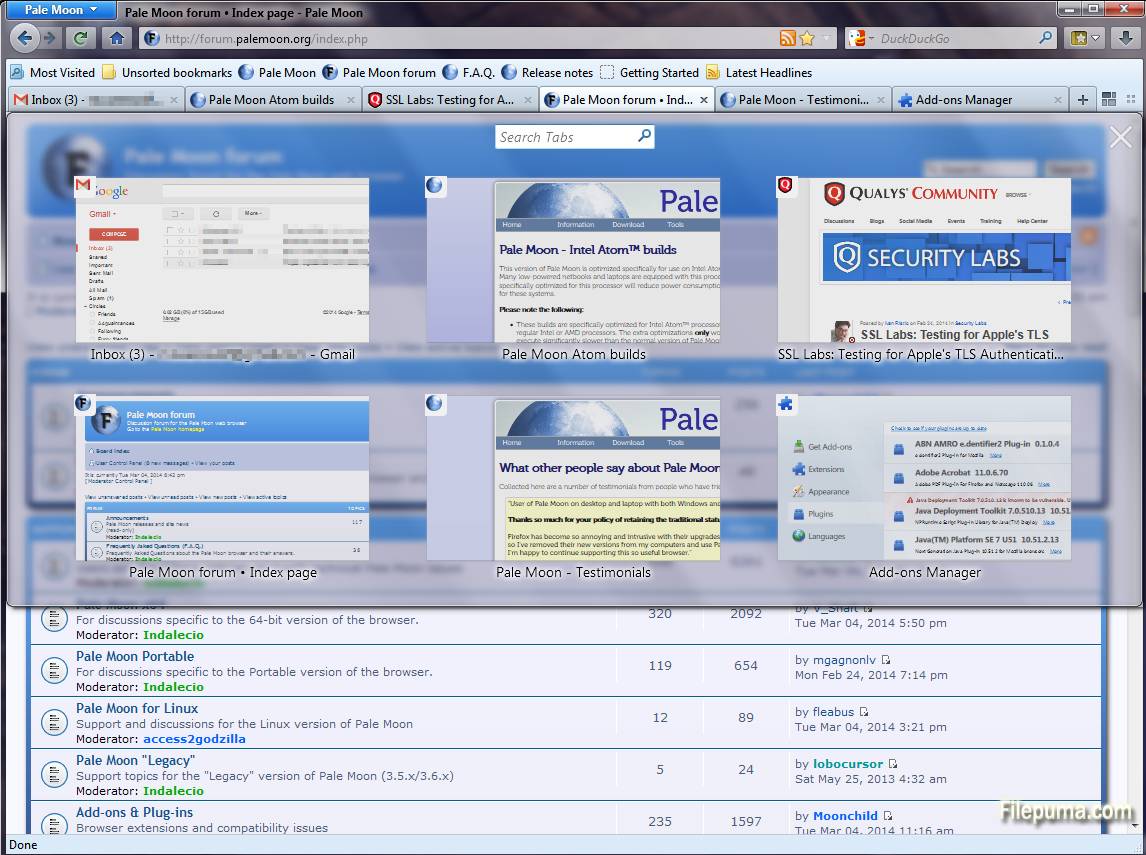
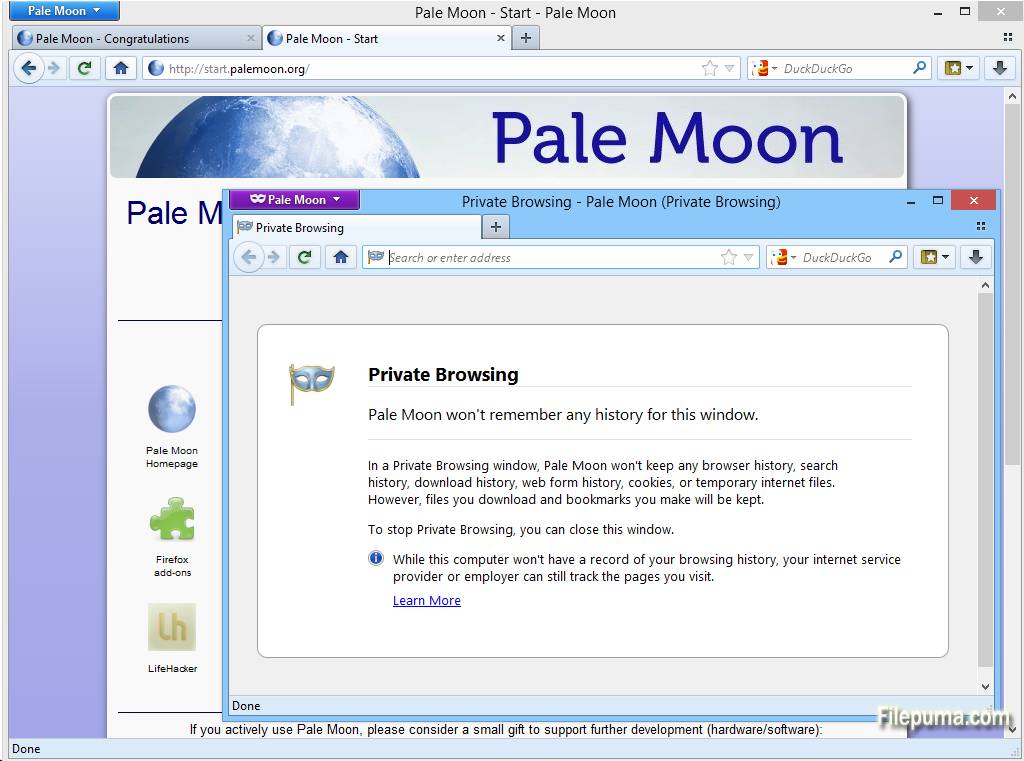
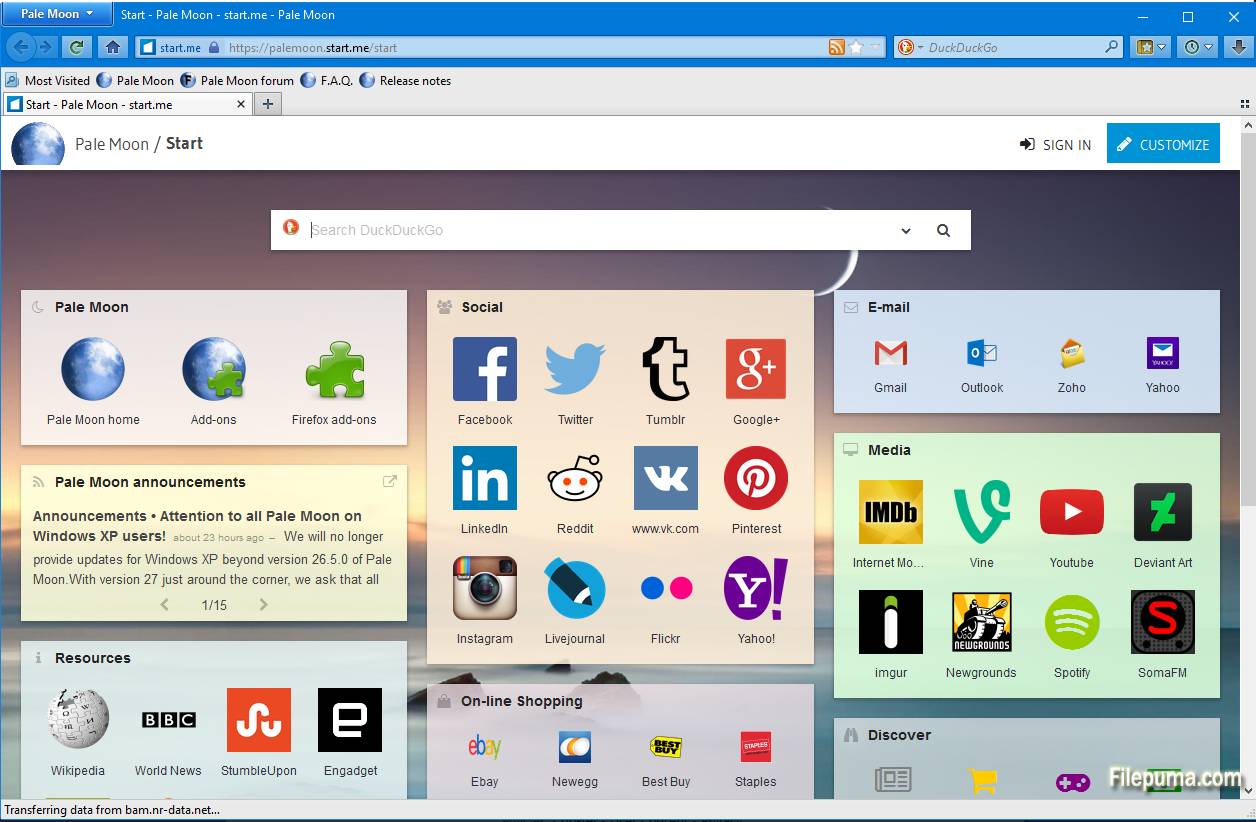


蒼月是一款基於Firefox的開源網頁瀏覽器,適用於Microsoft Windows,專注於效率和易用性。確保充分利用您的瀏覽器!
Pale Moon 為您提供一種瀏覽體驗,這是一個從源代碼構建的瀏覽器,具有精心挑選的功能和優化,以最大程度地提高瀏覽器的速度、穩定性和用戶體驗,同時保持與您喜愛和依賴的數千個 Firefox 擴展的兼容性。
這個瀏覽器雖然在運作方式上與Firefox相近,但提供了一組不同的功能。它禁用了幾個精心挑選但需求不高,且不會影響網頁顯示或運作方式的功能;這一切都是為了最大化瀏覽器的效率。請查看包含技術細節的頁面以了解瀏覽器支持和不支持的功能。例如,如果您需要無障礙功能或家長控制,請訪問Firefox主頁並獲取官方的非優化版本的瀏覽器。
主要特點:
Pale Moon 為您提供一種瀏覽體驗,這是一個從源代碼構建的瀏覽器,具有精心挑選的功能和優化,以最大程度地提高瀏覽器的速度、穩定性和用戶體驗,同時保持與您喜愛和依賴的數千個 Firefox 擴展的兼容性。
這個瀏覽器雖然在運作方式上與Firefox相近,但提供了一組不同的功能。它禁用了幾個精心挑選但需求不高,且不會影響網頁顯示或運作方式的功能;這一切都是為了最大化瀏覽器的效率。請查看包含技術細節的頁面以了解瀏覽器支持和不支持的功能。例如,如果您需要無障礙功能或家長控制,請訪問Firefox主頁並獲取官方的非優化版本的瀏覽器。
Pale Moon將繼續提供適當大小的分組導航按鈕、預設啟用的書籤工具列、緊挨著預設頁面內容的標籤頁(易於切換),以及至少沒有功能狀態欄和更多的自訂自由,僅舉幾個例子。
Pale Moon 是且將始終是開源的,可以完全免費下載和使用!
主要特點:
- 優化以適應現代處理器
- 基於包含我們自主優化的佈局和渲染引擎(Goanna)的Unified XUL Platform(UXP)
- 安全:源自成熟的Mozilla程式碼並定期更新最新的安全修補程序
- 安全:附加安全功能和安全意識的開發
- 由我們的用戶社群支持,並且完全非盈利
- 隱私意識:無廣告;無遙測、間諜軟體或數據收集
- 熟悉、高效、完全自定義的界面
- 支援完整主題:對任何元素設計有完全的自由
- 支持輕鬆創建的輕量主題(skins)
- 流暢且快速的頁面繪製和腳本處理
- 卓越的漸變和字體
- 將繼續支持 NPAPI 插件,如 Silverlight、Flash 和 Java
- 對不斷增加的 Pale Moon 專用擴展的支持
- 廣泛且增長的對現有網路標準的支持
最新消息
Version 25.8.0
Fixes/changes:
Security fixes:
Fixes/changes:
- Updated LibVPX to 1.4.x to be able to play more kinds of VP9-encoded videos.
- Updated the JPEG decoder library to 1.4.0.
- Fixed and cleaned up XPCOM timer thread code to avoid intermittent issues with events not firing (especially after stand-by).
- Updated overrides to work around issues with Facebook and Netflix.
- Fixed an issue where too-old system-supplied NSPR and/or NSS libraries would be accepted for use.
Security fixes:
- Updated the libpng library to 1.5.24 to address critical security issues CVE-2015-7981 and CVE-2015-8126
- Updated the NSPR library to 4.10.10 to address several security issues.
- Updated the NSS library to 3.19.4 to address several security issues.
- Fixed a memory safety hazard in SVG path code (CVE-2015-7199).
- Fixed an issue with IP address parsing potentially allowing an attacker to bypass the Same Origin Policy (CVE-2015-7188).
- Fixed an Add-on SDK (Jetpack) issue that would allow scripts to be executed despite being forbidden (CVE-2015-7187).
- Fixed a crash due to a buffer underflow in libjar (CVE-2015-7194).
- Fixed an issue for Android full screen that would potentially allow address spoofing (CVE-2015-7185).
- Added size checks in canvas manipulations to avoid potential image encoding vulnerabilities like CVE-2015-7189. DiD
- Fixed potential information disclosure vulnerabilities through the NTLM authentication mechanism. Insecure NTLM v1 is now disabled by default, and the workstation name is set to WORKSTATION by default (configurable with a preference for environments where identification of workstations is done by actual reported machine name). This avoids issues like CVE-2015-4515.
- Fixed a potentially vulnerable crash from a spinning event loop during resize painting. DiD
- Fixed several Javascript-based memory safety hazards. DiD
該程序提供其他語言版本
- Download Pale Moon (32bit)
- Télécharger Pale Moon (32bit)
- Herunterladen Pale Moon (32bit)
- Scaricare Pale Moon (32bit)
- ダウンロード Pale Moon (32bit)
- Descargar Pale Moon (32bit)
- Baixar Pale Moon (32bit)
使用者評價
用戶評分
4/5
 46
許可證:
免費
需求:
Windows Vista/ Windows 7/ Windows 8/ Windows 10/ Server 2008
語言:
English
尺寸:
20.4MB
出版社:
更新了:
Nov 17, 2015
清潔
報告軟體
最新版本
舊版本
 Pale Moon (32bit) 34.3.2
 Pale Moon (64bit) 34.3.2
 FossaMail (32bit) 38.2.0
 FossaMail (64bit) 38.2.0
 Pale Moon Portable (32bit) 34.3.2
 Pale Moon Portable (64bit) 34.3.2
 Google Chrome (64bit) 153.0.8010.48
 Google Chrome (32bit) 153.0.8010.48
 Mozilla Firefox (32bit) 156.0
 Mozilla Firefox (64bit) 156.0
 Maxthon (64bit) 7.5.3.2200
安全級別
為了避免對您的設備造成潛在損害,並確保您的數據和隱私安全,我們的團隊在每次新的安裝檔案上傳到我們的伺服器或連結到遠端伺服器時進行檢查,並定期審查該檔案以確認或更新其狀態。根據這種檢查,我們為任何可下載檔案設定以下安全級別。
 清潔
這個軟體程序極有可能是乾淨的。
我們在全球60多個主要殺毒服務中掃描了與此軟件程序相關的文件和網址;未發現任何潛在威脅。並且沒有捆綁第三方軟件。
 警告
本程序是由廣告支持的,可能會提供安裝不必要的第三方程序。這些可能包括工具欄、更改您的首頁、預設搜尋引擎或安裝其他第三方程序。這些可能是誤報,我們建議用戶在安裝和使用此軟體時要小心。
 殘疾的
這款軟體不再提供下載。這款軟體程式很可能是惡意的,或存在安全問題或其他原因。
提交報告
謝謝你!
您的報告已經發送。
我們將審查您的請求並採取適當的行動。
請注意,您將不會收到有關此報告所採取行動的通知。我們對可能造成的任何不便表示歉意。
我們感謝您在保持我們網站清潔和安全方面的幫助。