
Pidgin2.10.10
 免費下載
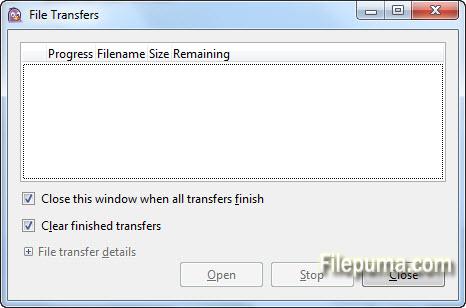
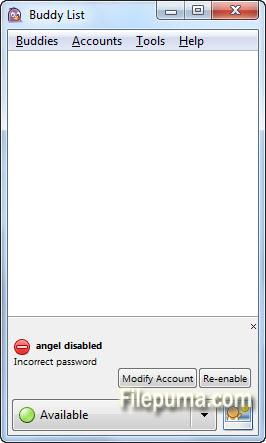
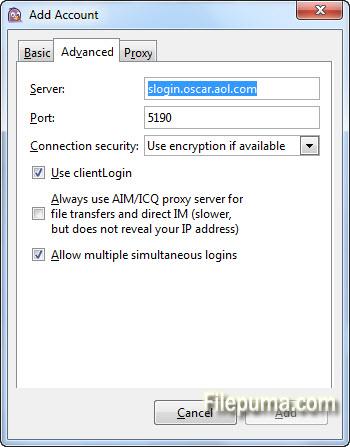
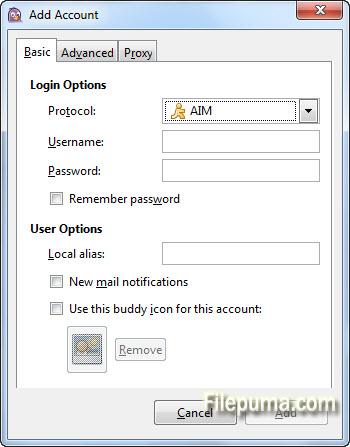


皮欽是一款廣泛使用的即時通訊應用程式,促進來自不同語言背景的用戶之間的溝通。以簡單和易用為設計理念,Pidgin 支援多種聊天協議,包括 AIM、ICQ、Google Talk、XMPP 等,允許用戶將多個帳戶整合到一個介面中。
Pidgin的一個關鍵特點是其自訂選項。用戶可以從多種主題和插件中選擇,來個性化他們的體驗,增強功能。不論是添加表情符號、整合加密以保護對話安全,還是擴展對其他聊天協議的支持,Pidgin都提供靈活性以滿足個人偏好。
Pidgin的另一個顯著特點是其開源性質,這促進了社區內的合作和創新。來自世界各地的開發者為其改進做出貢獻,確保定期更新和錯誤修復,以維持其可靠性和性能。
Pidgin 的使用者友好介面使其適合休閒和專業用途。它受到個人、企業和機構的青睞,成為尋求超越語言障礙的精簡通信平台的首選。
總之,Pidgin 作為一個多功能且易於使用的即時訊息解決方案,讓使用者能夠在不同的平台和協議間無縫連接和溝通。
主要特點:
- 支持多協議:同時連接到多個聊天網絡。
- 可自訂介面:用戶可以個性化主題、字體和佈局。
- 插件系統:透過可下載的插件擴展功能。
- 檔案傳輸:安全地在用戶之間傳送檔案。
- 表情符號和笑臉:聊天時可用的表情符號。
- 聊天記錄:記錄並保存聊天對話。
- 加密和安全性:支持私人對話加密。
- 狀態資訊:顯示線上、離開、忙碌或離線狀態。
最新消息
- Check the basic constraints extension when validating SSL/TLS certificates. This fixes a security hole that allowed a malicious man-in-the-middle to impersonate an IM server or any other https endpoint. This affected both the NSS and GnuTLS plugins. (Discovered by an anonymous person and Jacob Appelbaum of the Tor Project, with thanks to Moxie Marlinspike for first publishing about this type of vulnerability. Thanks to Kai Engert for guidance and for some of the NSS changes) (CVE-2014-3694)
- Allow and prefer TLS 1.2 and 1.1 when using the NSS plugin for SSL. (Elrond and Ashish Gupta)
libpurple3 compatibility
- Encrypted account passwords are preserved until the new one is set.
- Fix loading Google Talk and Facebook XMPP accounts.
Windows-Specific Changes
- Don't allow overwriting arbitrary files on the file system when the user installs a smiley theme via drag-and-drop. (Discovered by Yves Younan of Cisco Talos) (CVE-2014-3697)
- Updates to dependencies
- NSS 3.17.1 and NSPR 4.10.7
Finch
- Fix build against Python 3. (Ed Catmur)
Gadu-Gadu
- Updated internal libgadu to version 1.12.0.
Groupwise
- Fix potential remote crash parsing server message that indicates that a large amount of memory should be allocated. (Discovered by Yves Younan and Richard Johnson of Cisco Talos) (CVE-2014-3696)
IRC
- Fix a possible leak of unencrypted data when using /me command with OTR. (Thijs Alkemade)
MXit
- Fix potential remote crash parsing a malformed emoticon response. (Discovered by Yves Younan and Richard Johnson of Cisco Talos) (CVE-2014-3695)
XMPP
- Fix potential information leak where a malicious XMPP server and possibly even a malicious remote user could create a carefully crafted XMPP message that causes libpurple to send an XMPP message containing arbitrary memory. (Discovered and fixed by Thijs Alkemade and Paul Aurich) (CVE-2014-3698)
- Fix Facebook XMPP roster quirks.
Yahoo
- Fix login when using the GnuTLS library for TLS connections.
該程序提供其他語言版本
- Download Pidgin
- Télécharger Pidgin
- Herunterladen Pidgin
- Scaricare Pidgin
- ダウンロード Pidgin
- Descargar Pidgin
- Baixar Pidgin
使用者評價
用戶評分
 4
許可證:
免費
需求:
Windows All
語言:
Multi-languages
尺寸:
9.2MB
出版社:
更新了:
Oct 22, 2014
清潔
報告軟體
最新版本
舊版本
開發者的軟體
 Pidgin 2.14.14
 TeamSpeak Client (64bit) 3.6.2
 Telegram Desktop 7.2.8
 TeamSpeak Client (32bit) 3.6.2
 Signal 8.26.0
 Mumble 1.5.915
安全級別
為了避免對您的設備造成潛在損害,並確保您的數據和隱私安全,我們的團隊在每次新的安裝檔案上傳到我們的伺服器或連結到遠端伺服器時進行檢查,並定期審查該檔案以確認或更新其狀態。根據這種檢查,我們為任何可下載檔案設定以下安全級別。
 清潔
這個軟體程序極有可能是乾淨的。
我們在全球60多個主要殺毒服務中掃描了與此軟件程序相關的文件和網址;未發現任何潛在威脅。並且沒有捆綁第三方軟件。
 警告
本程序是由廣告支持的,可能會提供安裝不必要的第三方程序。這些可能包括工具欄、更改您的首頁、預設搜尋引擎或安裝其他第三方程序。這些可能是誤報,我們建議用戶在安裝和使用此軟體時要小心。
 殘疾的
這款軟體不再提供下載。這款軟體程式很可能是惡意的,或存在安全問題或其他原因。
提交報告
謝謝你!
您的報告已經發送。
我們將審查您的請求並採取適當的行動。
請注意,您將不會收到有關此報告所採取行動的通知。我們對可能造成的任何不便表示歉意。
我們感謝您在保持我們網站清潔和安全方面的幫助。